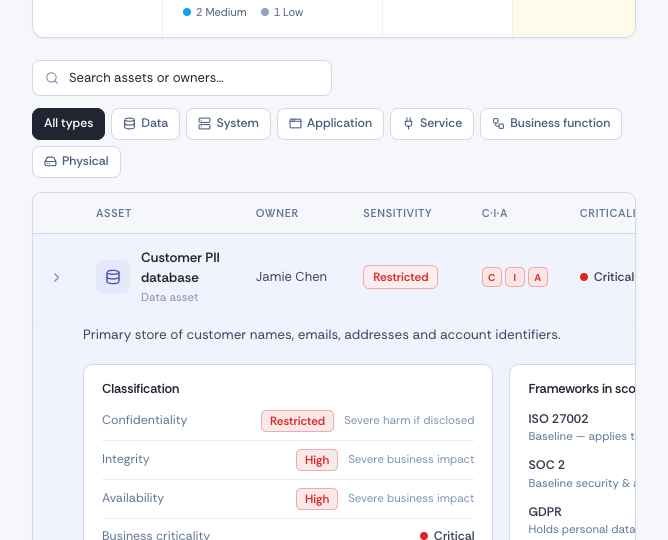
ZeroRisk maps every asset you protect to the regulations in scope — GDPR, ISO 27001, SOC 2, NIS2, DORA, CRA — then vets the vendors that touch them against each one. Pick the frameworks; we handle the rest.
Asset-driven
One scope, every framework.
Each asset is classified once and auto-mapped to the frameworks it falls under. Add a new regulation and your existing assets — and the vendors behind them — are instantly re-scoped against it.
A prospect’s security review asks for SOC 2 or ISO 27001 and the deal stalls. ZeroRisk gets you moving the same day: the gap report shows exactly what’s missing, the agent pre-fills the assessment and drafts the policies, and you work through a short review instead of a six-month project. No compliance hire needed.
You’re adding EU regulations on top
GDPR you had to do; now NIS2 or DORA lands on top. Because every control you already run is mapped once and reused, the next framework starts largely pre-filled — the agent shows only the genuinely new requirements. Adding a regulation stops meaning starting over.
You’re a financial entity under DORA
The ICT third-party register, contract-provision checks and concentration-risk view DORA expects are generated from your vendor list and kept current daily — the register exports whenever your regulator asks.
You ship products with digital elements
The Cyber Resilience Act phases in through 2027. The agent maps its essential requirements — secure development, vulnerability handling, update obligations — against your practice and drafts what’s missing, so the deadline arrives as a checklist, not a crisis.
FAQ
Choosing your path
Start with the one your customers ask for: SOC 2 if you sell to US companies, ISO 27001 for European and enterprise buyers, GDPR if you process EU personal data (that one isn’t optional). The free gap report shows your distance to each, which usually makes the choice obvious.
Yes — that’s the core of the model. Controls, policies and evidence are mapped once and reused everywhere, so your second framework typically starts more than half pre-filled. Plans upgrade in place when you add scope.
That’s the design target. The agent does the scoping, pre-filling and drafting; your part is reviewing and signing, which fits inside a founder’s or ops lead’s week. Support and onboarding are included on every plan.
It depends on what the gap report finds — which is why it comes first and free. Teams starting from spreadsheets usually spend their time deciding and signing rather than writing; the agent has the drafting done from day one.