The platform

One agent for your whole compliance program — your readiness and your vendors.

From the assets you protect, to the vendors that touch them, to the signed evidence an auditor accepts — ZeroRisk runs the whole chain for you, every day.

Book a demo Browse vendor library
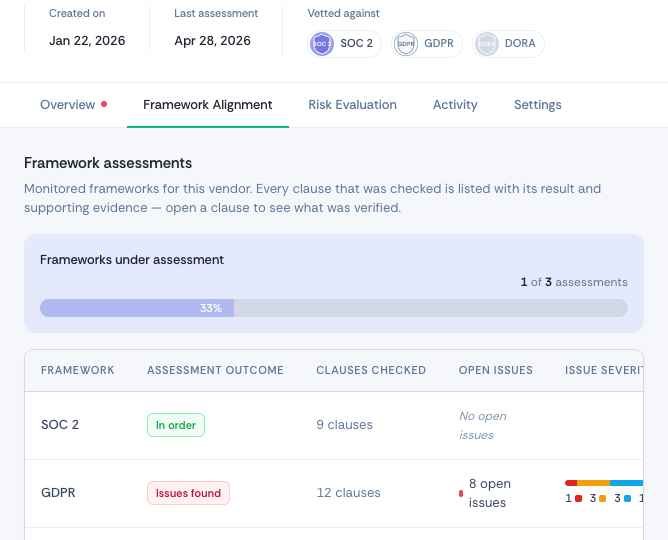
app.zerorisk.com/vendors/adyen
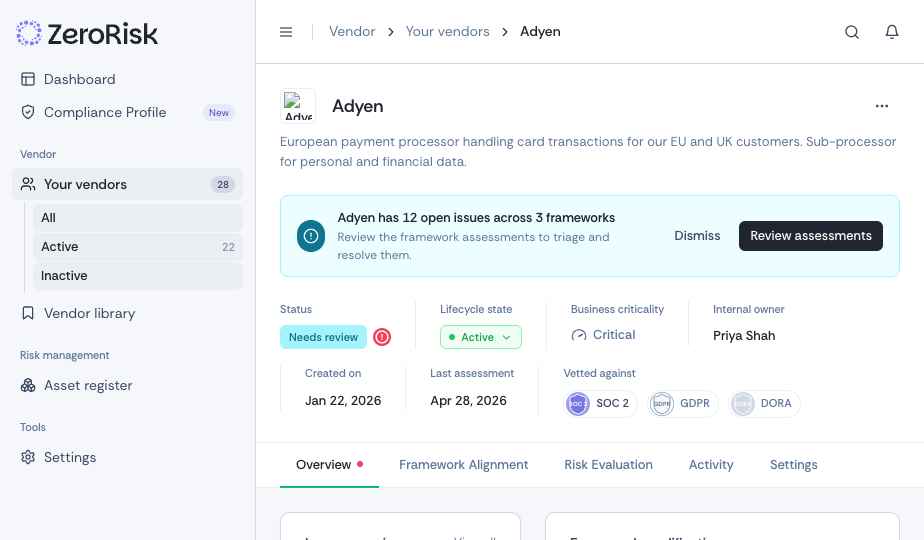
ZeroRisk vendor profile showing open issues across frameworks
The platform

Four jobs. One continuous system.

Most tools do one slice and hand you the rest. ZeroRisk connects all four — so nothing falls between the gaps.

Asset register

Start from what you actually protect.

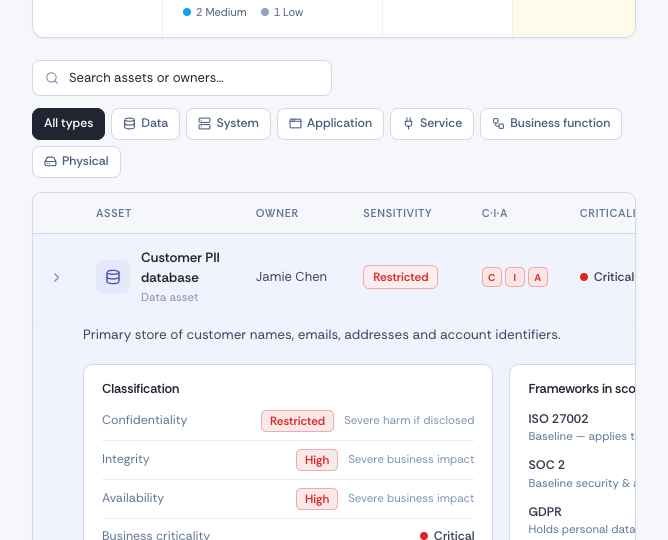
Capture every dataset, system and business function once. Classify each for confidentiality, integrity and availability — and ZeroRisk works out which frameworks it falls under.

Your vendor vetting is scoped from here, so you assess the right vendors at the right depth — never by guesswork.

  • C·I·A classification with business criticality
  • Auto-mapped to GDPR, ISO 27001, SOC 2, NIS2, DORA & CRA
  • Every asset linked to the vendors that handle it
app.zerorisk.com/asset-register
Asset classification, frameworks in scope and the vendors handling it
Vendor vetting

Every vendor, vetted clause by clause.

Each vendor is assessed against every framework it’s in scope for. Open issues surface first; the full clause-by-clause record sits one tap away.

It’s a written verdict, not a security score — with the evidence that backs each result attached.

  • Framework Alignment & Risk Evaluation per vendor
  • Open issues triaged across frameworks
  • Every finding carries its own audit trail — who resolved, tolerated or reopened it, and when
  • Lifecycle, criticality & internal owner tracked
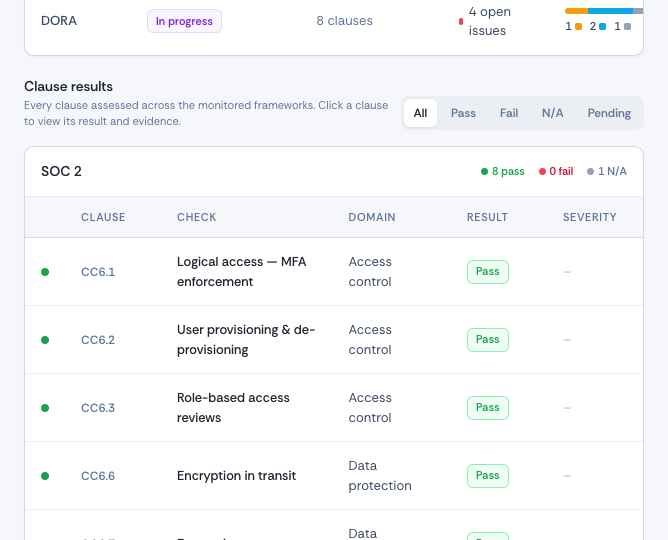
app.zerorisk.com/vendors/adyen · Framework Alignment
Framework assessments: SOC 2 in order, GDPR issues found, DORA in progress
Findings at scale

Hundreds of findings, handled.

Hundreds of clauses across every monitored framework, in one queryable view. Filter by result, sort by severity, page across frameworks — open issues always lead.

We triage and remediate with you so the list only ever shrinks.

  • Every clause assessed, with pass / fail / N·A / pending
  • Filter, sort and search across the whole portfolio
  • Evidence attached to every result
app.zerorisk.com/vendors/adyen · Clause results
Clause-by-clause results table with evidence
Audit-ready proof

Proof an auditor accepts.

Every vendor carries a complete, current record. Your whole portfolio rolls up into one signed Vendor Security Assessment Certificate — framework-mapped and dated.

When auditors ask for evidence, you export it. It’s already done.

  • Per-vendor criticality & status at a glance
  • Framework-specific risk interpretations
  • One-click export, always up to date

Vendor Security Assessment Certificate

Issued to

ABC Corporation

VendorCriticalityStatus
AdyenCriticalNeeds review
AWSHighIn order
OktaHighNeeds review
SalesforceHighIn order
GDPRISO 27001SOC 2NIS2DORACRA
ZeroRisk Issued · Jun 28, 2026
New — the Readiness agent

Your own compliance, run by the agent.

Point it at your organization and get a pre-filled assessment, drafted fixes and an audit-ready file — for SOC 2, ISO 27001, GDPR, DORA, NIS2 and the EU Cyber Resilience Act.

Pre-filled assessments

The agent answers every requirement it can — from your profile and the documents you upload, each with a confidence score. You confirm in a short interview.

Scope that forms around you

Answer a handful of scoping questions once; requirements that don’t apply go N/A automatically. No irrelevant checklists.

Drafted controls & policies

Every gap ships with an agent-drafted control and full policy text — edit inline, adopt in one click.

Evidence library

Drag-and-drop artifacts once, link them to any control. The agent reviews whether evidence actually proves what it claims.

Verdicts you can defend

Nothing counts as done without a control, evidence and a named human signature — and every control has an owner on record.

Cross-framework coverage

One control counts everywhere it applies — a coverage view shows exactly what each control proves across frameworks. Your second framework starts mostly done.

Audit package, one click

Export a signed, evidence-backed PDF of your posture — any day of the year, not just audit week.

Live readiness dashboard

Per-framework readiness rings on your home dashboard — the number stays honest as evidence ages.

Run your first gap report free
New — People & Access

Who has access to what — reviewed, signed, evidenced.

A staff directory, an access map across your systems, and reviewer-driven certifications that produce the exact evidence ISO 27001 A.5.18 and SOC 2 CC6.2/CC6.3 ask for — plus a portal where every employee confirms their part, no extra seats needed.

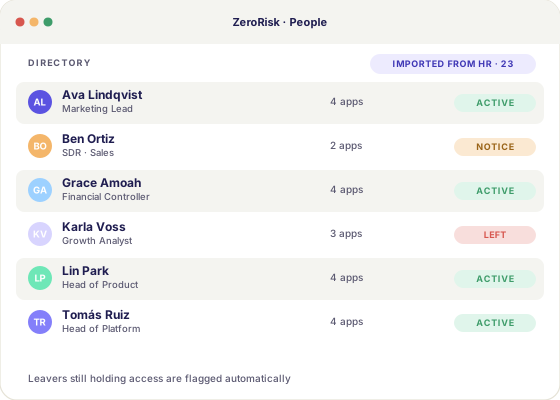
ZeroRisk staff directory with employment status and access counts
The whole workforce in one directory — imported from your HR export, leavers flagged the moment they still hold access.
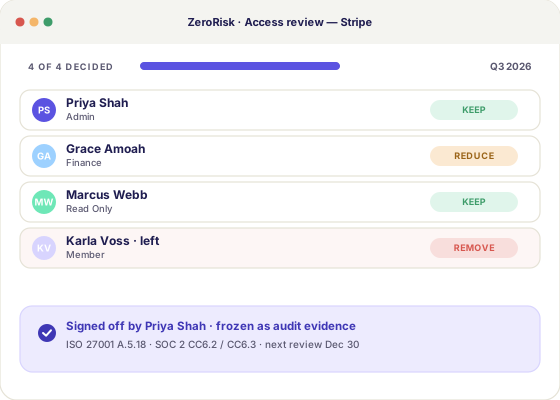
Access review sign-off producing a certified evidence snapshot
Reviews take minutes: keep / reduce / remove per person, one signature, and the snapshot becomes audit evidence.
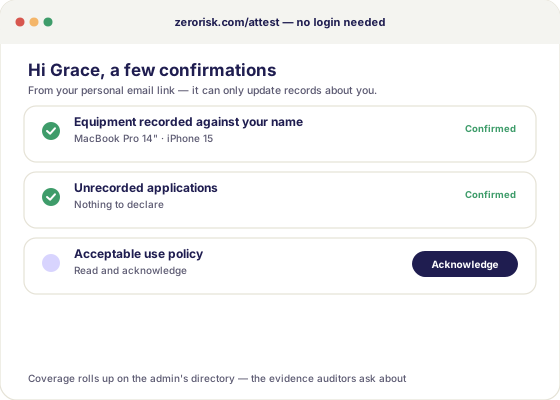
Personal attestation page reached from an email link, no account needed
Every employee confirms equipment, applications and the policy from a personal email link — no account, no seat.

Staff directory

Import any HR export — CSV or Excel, any delimiter. Every row is validated and held for your review before a single record is written.

Access map

Every system linked to your vendor register, every person’s access recorded in the system’s own permission wording.

Access reviews on your cadence

The system owner works the user list — keep, reduce, remove — and signs, every 3 to 24 months per system. The frozen snapshot is the evidence an auditor asks for.

Changes followed through

Remove verdicts become a tracked queue: the owner gets an email, applies the change, and the record shows who closed it and when.

Leavers can’t hide

A departed employee still holding access is flagged as a finding — it cannot be parked as out-of-scope or dressed up as certified.

Equipment register

Devices recorded per person with an issue/return lifecycle — and each person confirms their own record once a year.

Attestations without seats

Personal email links let all staff confirm their details and equipment, declare shadow IT and acknowledge your policy — no login, coverage tracked.

Roles that mean something

Reviewers see only the systems they own; employees see only their own tasks — enforced server-side, not hidden in the UI.

See it on your org
New — Risk management

Your risk register writes itself. You sign it.

The formal core of an ISMS — the risk assessment, the treatment plan and the Statement of Applicability — drafted from records ZeroRisk already holds, and signed by named people. The documents ISO 27001 6.1, SOC 2 CC3, DORA Art. 6, NIS2 Art. 21 and GDPR Art. 32 all ask for.

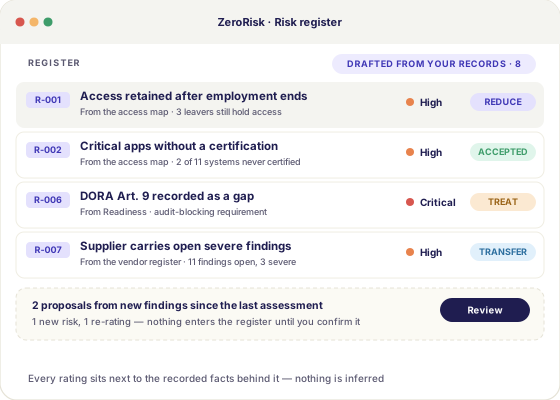
Risk register drafted from vendor findings, readiness gaps and the access map
The register arrives populated — every risk drafted from facts already recorded, never a blank page to brainstorm.
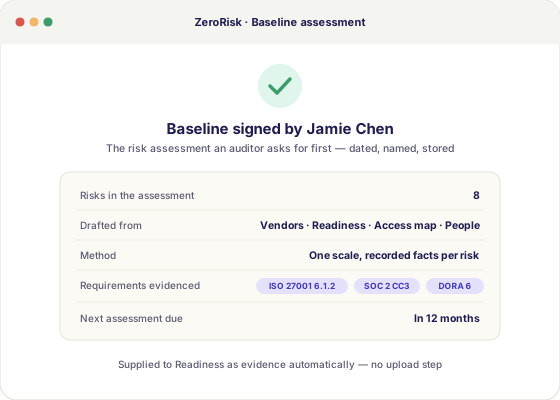
Signed baseline risk assessment receipt with method and requirements evidenced
Review the draft, adjust ratings and owners, sign once — the receipt is the risk assessment an auditor asks for first.
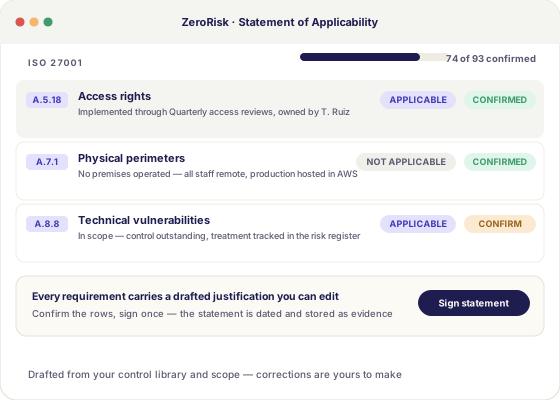
Statement of Applicability with drafted justifications per requirement
The Statement of Applicability drafts itself from your controls and scope — you confirm each row and sign one statement.

Arrives populated

Risks are drafted from your vendor findings, readiness gaps, access map and people records — leavers holding access, uncertified systems, suppliers with open findings.

Facts, not scores

One severity scale, and the recorded facts printed next to every rating. The system’s proposal stays on record beside your change — nothing is inferred.

Treatment through your controls

Reduce, accept, transfer or avoid — the four ISO 27001 options. Treatment links the controls you already run, so the plan and the evidence can’t drift apart.

Appetite with a named authority

One org-level threshold. Residual risk above it can only be accepted by the person you name — a dated, signed record every time.

Statement of Applicability, drafted

Applicability and justification pre-written per requirement from your scope and control library. Confirm each row, sign once, export.

A plan that can’t go stale

The treatment plan is a live view of the register — decision, control, owner, agreed date — never a second list to keep up to date.

Owners work from the portal

Risk owners see their duties — decide a treatment, sign an acceptance — under their own login, without an admin seat.

Anyone can report something

A lost device, a suspicious email — every employee can raise it from their portal in two minutes, recorded under their own name and ready to triage.
See it on your org
Done-for-You

You set the scope. We run the platform.

ZeroRisk isn’t a dashboard you have to operate. Real GRC operators run the assessments, the monitoring and the evidence — guided by experts, powered by automation.

Verified, audit-ready results without chasing vendors or updating spreadsheets.

Hand over vendor risk today
What you get

Your third-party risk, fully handled

Asset-driven scoping

Vetting scoped from what you actually protect — so nothing material is missed.

Clause-by-clause vetting

A written, evidence-backed verdict for every framework a vendor is in scope for.

Vendors checked daily

Re-checked every 24 hours, with alerts only when something actually moves your risk.

ZeroRisk Certificates

One signed certificate for your whole portfolio — ready for regulators and auditors.

10,000+ vendors pre-mapped

Or upload your own list — we map every entity to its compliance scope.

Up to 80% more cost-effective

And far faster than manual processes — without cutting corners on coverage.

Onboarding

Live in five minutes

1

Add your assets & frameworks

Describe what you protect, or pick your frameworks — GDPR, ISO 27001, SOC 2, NIS2, DORA, CRA. ZeroRisk scopes the rest.

2

Hand over your vendors

Option A · Pick from our library
  • 10,000+ pre-mapped vendors
  • Just click to add
  • Instant activation
Option B · Upload your list
  • CSV, Excel, whatever you have
  • We map and vet the rest
  • New vendors live in 24 hours
3

Complete oversight, zero manual effort

  • Clause-by-clause assessments & audit records
  • Breach & incident alerts
  • Security & policy changes
  • Financial due diligence
  • Framework & regulation tracking
FAQ

What buyers ask us

Automation watches your stack and gives your team the to-do list. ZeroRisk’s agent does the items: it pre-fills the assessment, writes the missing policies, and monitors your vendors — your team reviews and signs. See the honest comparisons: ZeroRisk vs Vanta, vs Drata, vs Secureframe.
Decide and sign. The agent prepares every assessment answer, control and policy as a draft with a confidence score; a person you designate reviews, edits where needed, and signs. Expect focused review sessions instead of blank questionnaires.
Yes — vendor risk is native, not a module. Daily monitoring, clause-by-clause vetting and the 10,000+ vendor library run on the same platform and control set as your own certification readiness, on every plan.
No. Every employee confirms their equipment, declares shadow IT and acknowledges your policy from a personal email link — no login, no seat, no license. Coverage rolls up for the auditor automatically.
You export the audit package: scoped requirements, controls, evidence and the named human signature on every verdict, current as of that day. It works with any auditor — there’s no lock-in to a partner network.

Compliance is mandatory.
Doing it yourself isn’t.

  • Every vendor mapped to the assets and frameworks it touches.
  • Clause-by-clause verdicts, backed by evidence.
  • Monitored every 24 hours. Certificate always current.
  • In 5 minutes, vendor risk becomes our problem, not yours.
Book a demo