ZeroRisk’s agent learns your business, scopes out what doesn’t apply, pre-fills every assessment, drafts the controls you’re missing, and keeps watch over your vendors — you review, sign, and walk into audits already done.
Never touch a compliance spreadsheet again

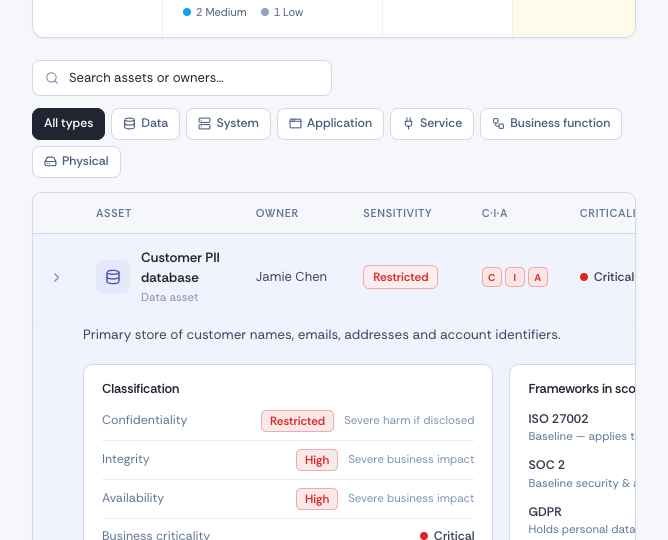
Most tools start with a vendor list. ZeroRisk starts with your asset register — every dataset, system and business function, classified once for confidentiality, integrity and availability.
From there we work out which frameworks each asset falls under, and exactly which vendors need vetting — and how deeply. Scope stops being guesswork.

Most companies have between 50–200 vendors — and underestimate the count.
aren’t confident they know their full vendor list
hired a vendor that suffered a breach in the past 2 years
had a vendor-originated cyber breach last year
faced a third-party data breach in the last 12 months
That’s before you touch a single other compliance task.
Point it at your business once. The agent scopes, pre-fills, drafts and monitors — you review and sign.
Add your assets and answer a handful of profile questions. You get a framework applicability report — required, recommended or not applicable, per regulation — and anything that doesn’t apply goes N/A by itself.
The agent answers every requirement it can — from your profile and the documents you upload — each with a confidence score. You confirm the rest in a short interview, never a blank questionnaire.
Every gap ships with an agent-drafted control and policy. Attach or link evidence once — one control counts across every framework you run.
Nothing is “done” without a control, evidence and your signature. Vendors stay monitored daily; the audit package exports any day of the year.


Most tools cover your vendors or your own certification. ZeroRisk’s agent runs both — on the same evidence, the same controls, the same audit trail.
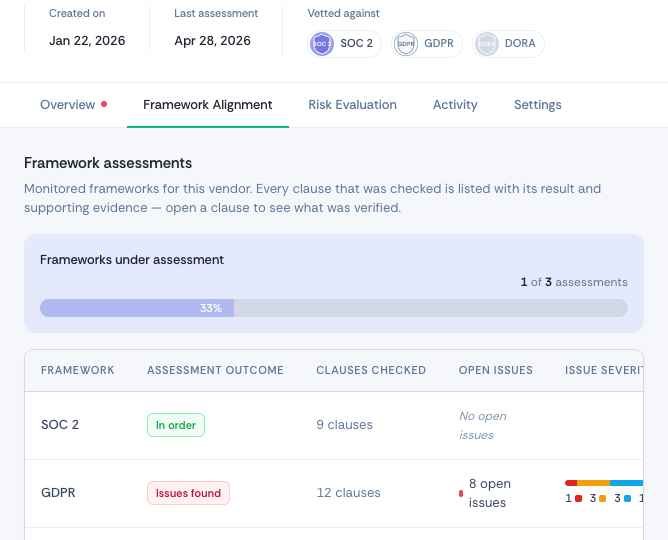
SOC 2, ISO 27001, GDPR, DORA, NIS2 — assessments pre-filled by the agent, a risk register and Statement of Applicability drafted from your own records, proven with evidence, signed by you.
Every vendor vetted clause-by-clause and re-checked daily — 10,000+ pre-monitored, verdicts in writing.
The agent drafts — humans decide. Every verdict is attributed, timestamped and backed by evidence an auditor accepts. No AI claims in your audit file.
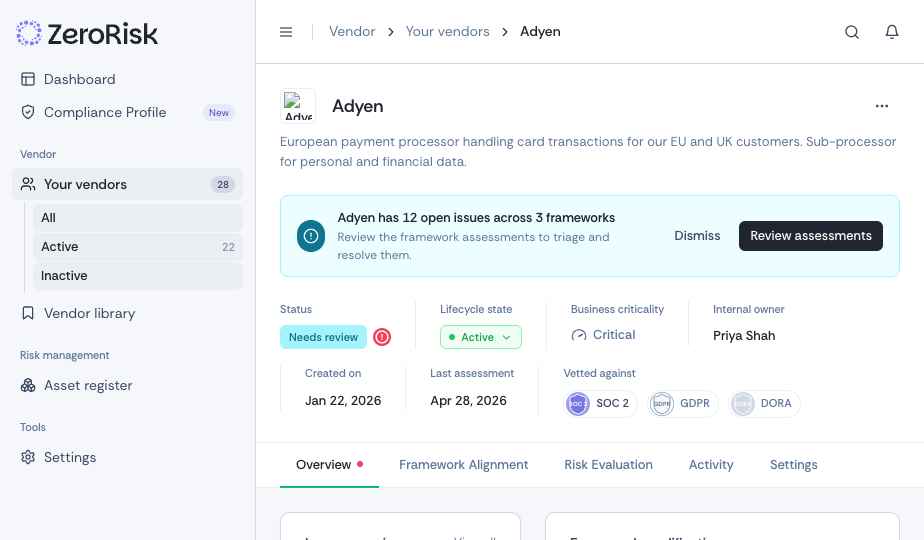
Not a security score. A written, evidence-backed verdict for every clause across every framework a vendor is in scope for.

Open issues lead. We work with you to remediate or document — and the row clears.
Every vendor re-checked every 24 hours — certificates, breaches, policy & financial changes.
10,000+ vendors pre-mapped. Click add — monitoring activates instantly.
No noise. Just the changes that move your risk — surfaced the moment they happen.
Prices shown billed annually — save 20% vs monthly. Every plan starts with the free gap report.
By the time auditors arrive, ZeroRisk has already done the work. Every vendor carries a complete, current record — and your whole portfolio rolls up into one signed certificate.
Issued to
ABC Corporation
| Vendor | Criticality | Status |
|---|---|---|
| Adyen | Critical | Needs review |
| AWS | High | In order |
| Okta | High | Needs review |
| Salesforce | High | In order |
Curious how deep our reviews go? Send us one of your key vendors and we’ll send you a full ZeroRisk Vendor Review — free.
Answer a few questions about your organization — the agent maps your frameworks and gaps, vendors included.
Get your free gap report10 minutes · no payment details · report lands in your inbox
Reminder: Every day you manage vendors manually is a day wasted. Every day without monitoring is a compliance risk.